[docs]: Add general notice that all requested API data is sent to client without filtering
Summary
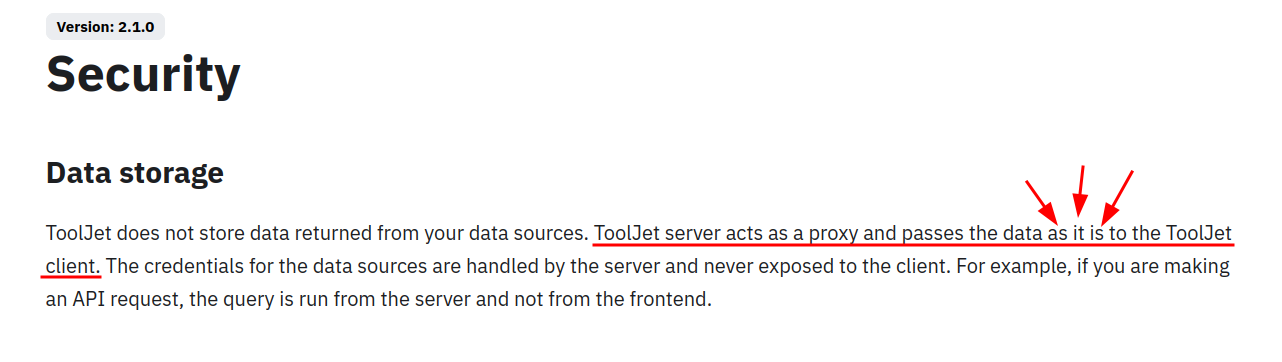
While working extensively with the baserow.io implementation of ToolJet I noticed that all API responses are sent to the client machine (web browser) without the ability to be filtered on server-side. As this might lead to unwanted exposure of data there should be a warning about that fact in the docs.
Currently the section "Security" is not highlighing this fact in a noticable manner (from my perspective) so that everybody is aware of that fact:
Issue Type
Documentation feature/update
The entire URL of the documentation with the issue
https://docs.tooljet.com/docs/security/
Steps to reproduce the issue
Additional Information
As this does not happen with SQL (I think so) the notice does not make sense there. Maybe we could place a general notice / warning about that fact in the docs of every implementation where this happens like baserow.io and others. And there should also be a noticable warning inside the Security section.
I also opened a feature request for server-side API preprocessing here: https://github.com/ToolJet/ToolJet/issues/5617
If the issue is confirmed, would you be willing to submit a pull request?
Yes
Code of Conduct
- I agree to follow the ToolJet Code of Conduct
Source: ToolJet/ToolJet