Claude Code in CI: Running Agentic Code Review, Test Generation, and Auto-Fix on Every Pull Request This article was written with the assistance of AI, under human supervision and review.
Why Agentic Code Review in CI Changes Everything Most CI failures waste hours on manual intervention because traditional bots flag problems but never fix them.
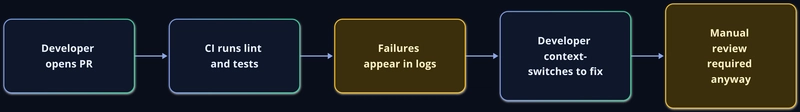
Developers open a pull request, the linter fails, tests break, and someone must context-switch from their current work to diagnose and patch the issue.
This context-switching compounds across teams until the cost of maintaining CI hygiene exceeds the value it provides.
Claude Code running in auto mode solves this by operating as an autonomous agent inside the CI pipeline.
When a pull request triggers the workflow, Claude Code reviews the diff, generates missing tests, attempts to fix failures, and posts structured feedback as review comments—all without human intervention.
The developer receives actionable fixes instead of error logs.
This distinction is critical.
Traditional CI bots detect and report.
Agentic CI detects, repairs, and documents.
The ROI appears in two places: reduced time-to-merge for routine issues and preserved cognitive capacity for architectural decisions that actually require human judgment.
Key Takeaways Claude Code in auto mode runs unattended in CI pipelines with a safety classifier blocking dangerous commands before execution.
Agentic CI performs code review, test generation, and auto-fix in a single workflow—eliminating the manual context-switch loop.
Production deployments require cost controls (token budgets per PR), scoped file permissions, and exit conditions to prevent runaway execution.
GitHub Actions, GitLab CI, and Azure DevOps all support Claude Code integration through environment variables and secrets management.
The pattern that works now is scoped, single-responsibility agents—one for review, one for test generation, one for auto-fix—not a single agent attempting all tasks.
Claude Code in Auto Mode: Running Unattended in CI Pipelines Auto mode enables Claude Code to execute commands without interactive confirmation.
The agent receives a task, plans a sequence of operations, and runs them to completion while a classifier model reviews each command for scope escalation or filesystem access beyond the defined boundaries.
This safety layer matters in CI because the agent operates with repository write access and environment secrets.
The failure mode here is subtle but expensive.
Without auto mode, Claude Code pauses for interactive approval on every command.
In CI, no terminal exists for interaction, so the workflow hangs until timeout.
With auto mode enabled, the agent proceeds to completion or hits a safety block, either of which produces a usable outcome for the pull request.
Configuring auto mode requires setting the environment variable and defining a permission scope in the workflow manifest.
The scope restricts which files the agent can read or modify.
A code review agent should see the entire diff but write only to a temporary comment file.
A test generation agent needs read access to source files and write access to test directories.
Setting Up Claude Code for Pull Request Reviews The entry point for agentic CI is a GitHub Actions workflow that triggers on pull request events.
The workflow checks out the repository, installs Claude Code, and invokes it with a task description tied to the specific PR diff.
This configuration separates concerns cleanly.
The variable prevents the agent from modifying source files during review.
The task description anchors the agent's focus on specific quality dimensions.
The GitHub Script action posts results as a comment, preserving them in the PR timeline for future reference.
The review step runs in parallel with existing CI checks.
If the build fails, Claude Code still performs its review based on the diff.
If tests fail, a separate workflow handles auto-fix.
This parallel execution reduces total pipeline time compared to sequential stages.
Auto-Generating Tests and Auto-Fixing Failures in CI Test generation and auto-fix require write access to the repository, which introduces risk if the agent produces malformed code.
The mitigation strategy is a two-phase workflow: the agent writes to a feature branch, then a human reviews the agent's commit before merging to the target branch.
The environment variable caps the agent's total token usage for this task.
Without this limit, a runaway loop—where the agent generates code that introduces new failures, then attempts to fix those failures—can consume quota rapidly.
A budget of 50,000 tokens typically covers diagnosis, code generation, and verification for most test suites.
The pattern here is defensive.
The agent writes to a separate branch, never directly to the PR branch.
This creates a manual approval gate: a developer reviews the auto-fix PR, confirms the changes are correct, then merges them into the original PR.
If the auto-fix introduces regressions, the developer closes the auto-fix PR and addresses the issue manually.
For test generation specifically, the task description should reference the existing test suite's patterns.
If the project uses Vitest with a particular assertion style, the prompt must include an example.
Without this anchoring, Claude Code defaults to generic Jest patterns that may not match the project's conventions.
Comparison: Claude Code vs Traditional CI Bots vs Manual Review Traditional CI bots detect violations but never repair them.
Manual review catches issues but scales poorly as teams grow.
Claude Code occupies a middle ground: it automates repairs for mechanical issues while flagging complex problems for human review.
The implication here is that agentic CI does not replace human review for architectural decisions, security boundaries, or product requirements.
It replaces the rote work of fixing lint errors, adding missing null checks, and generating boilerplate tests.
The time savings compound when a team merges dozens of PRs per day.
Traditional bots excel at consistency.
They enforce style rules without fatigue.
Agentic CI excels at remediation.
It applies fixes that follow the same patterns a human would use, but without the context-switching cost.
Manual review excels at judgment.
A human catches the security implication of a seemingly innocuous change that no static analysis tool flags.
The effective pattern combines all three.
Traditional bots run first as a fast gate.
If they fail, Claude Code attempts auto-fix.
If auto-fix succeeds, the PR proceeds to manual review for non-mechanical concerns.
If auto-fix fails, the developer receives both the bot's report and Claude's analysis of why the fix did not converge.
Production Patterns: Cost Control, Scoped Permissions, and Safety Classifiers Deploying agentic CI in production requires three controls: token budgets to prevent runaway costs, scoped file permissions to limit blast radius, and safety classifiers to block dangerous operations.
Token budgets sit at the repository level or per-PR level depending on billing constraints.
A per-repository monthly budget prevents a single malicious or misconfigured PR from exhausting the organization's quota.
A per-PR budget ensures fair resource distribution when multiple PRs arrive simultaneously.
The tradeoff is complexity: per-PR budgets require state tracking across workflow runs, typically stored in repository secrets or a database.
Scoped permissions use glob patterns to define read and write boundaries.
A review agent needs but .
A test generation agent needs and .
A refactoring agent needs broader write access, so its budget should be lower and its outputs should always land on a review branch.
Safety classifiers run before command execution.
The classifier model evaluates whether a command attempts to escalate privileges, access network resources, or modify files outside the declared scope.
If the classifier flags a command, the agent receives